

Members
A project has members, and a member has one of four roles:
| Role | May |
|---|---|
owner | one per project. Everything a manager does, and alone: change or remove a manager, rename the project, move it into a company, connect Storage, set up Integrations and AI keys, define custom fields and environments, delete from the Bin for good, and transfer ownership |
manager (Manager) | everything a member does, and runs the people below the owner: invites people, gives roles up to Manager, removes members and read-only people. Also restores from the Bin and deletes other people’s comments. No keys, no storage, no integrations |
member | works in the project: cases, suites, runs, plans, results, comments. Manages nobody |
reader (Read-only) | look, comment and propose in the review queue. Every other write is refused at the boundary, before a handler runs |
The person who creates a project is its owner. Their default project is theirs the same way. A project has exactly one owner at a time. Nobody demotes or removes the owner: ownership moves only by a transfer the new owner accepts or a move to another company the new owner accepts.
A company above projects has the same four role names — owner, manager, member, read-only — as a separate list from these: a company role opens no project, it only decides who may join or invite into the company’s projects and with which of these roles — see Companies → Roles.
Inviting somebody
Section titled “Inviting somebody”Settings → Members, the Invite form — an address and a role. Or:
POST /v1/members { "email": "tester@example.com", "role": "member" } → 201The owner or a manager invites. The role is manager, member or reader; owner is refused with
400 and the code use_handover — nobody is made the owner by an invitation or a role change, only
by a transfer.
Two outcomes, told apart by kind in the answer:
member— the address already has a Plune account: they are in at once, and the answer is their row.invitation— nobody has signed in with that address yet: a row waits on the Pending list, a mail says where to sign in, and the sign-in itself turns the invitation into a membership with the role it was sent with. No token travels in the mail: the magic link is the proof, and the invitation is what lets the address ask for one.
The address is lower-cased before it is compared or stored. Inviting the same address twice, or
one already in, answers 409; so does a project at its member limit (200).
In a company’s project
Section titled “In a company’s project”A project that belongs to a company says so on its Settings → Members, right under the hint: Checkout web is in Acme QA, the company’s name a link to its page. A project of no company says nothing of the kind.
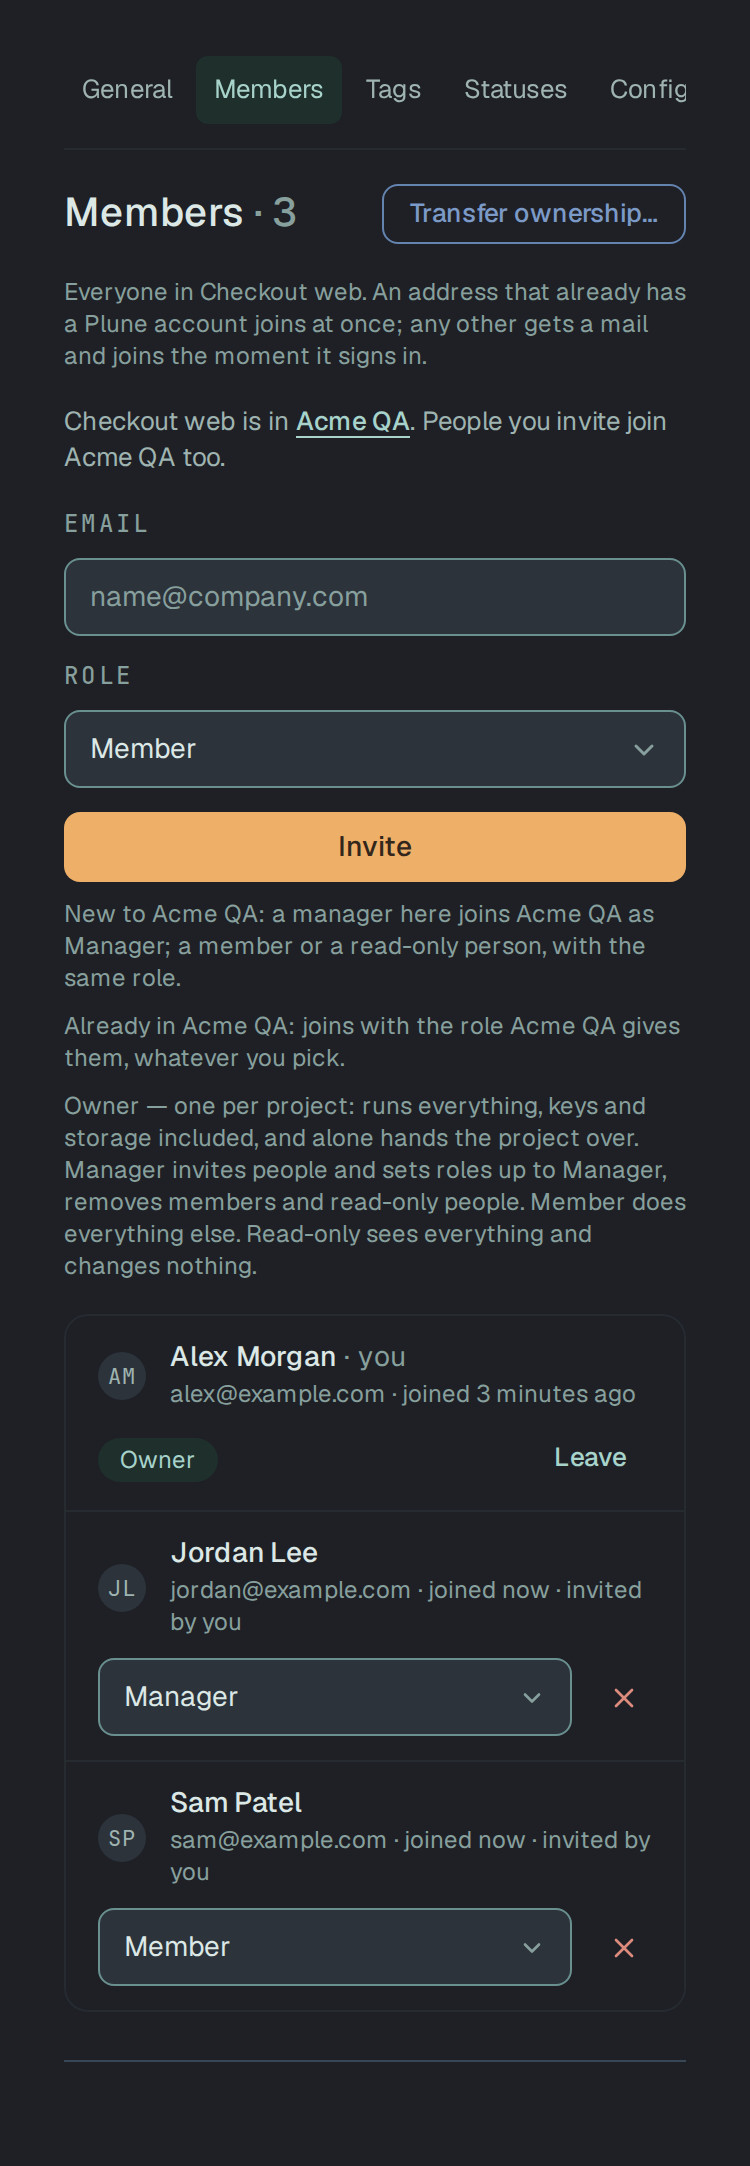
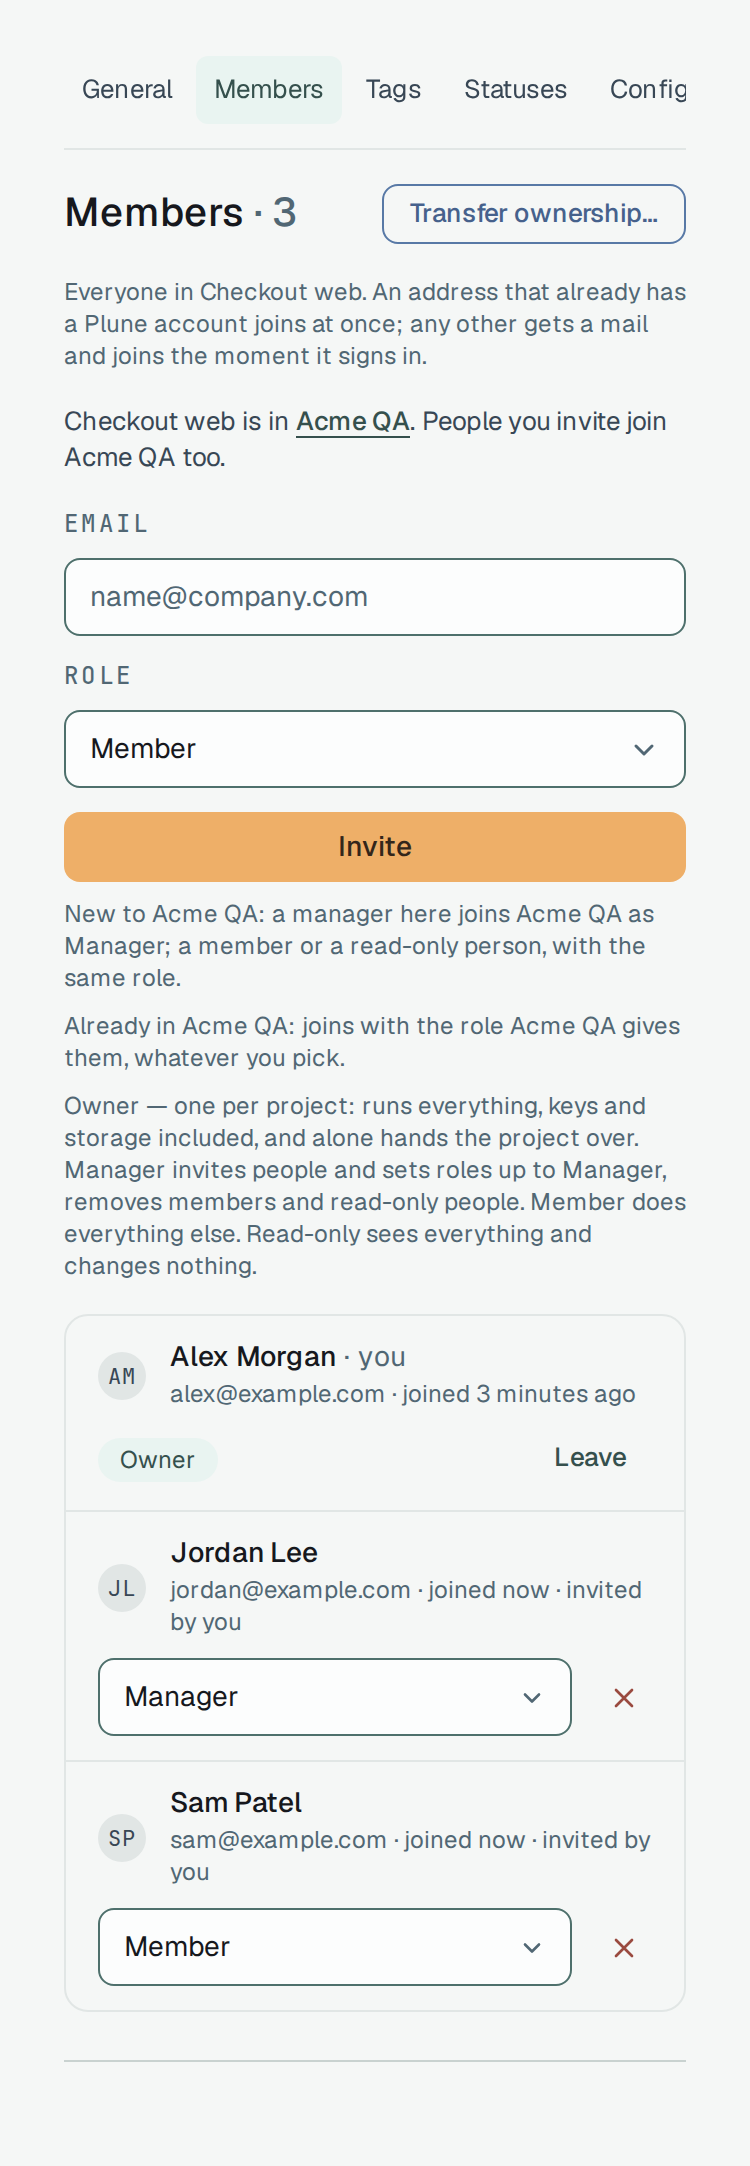
Who runs its people. Asking somebody in, changing a role and removing somebody belong to the company’s owner and managers — and only when they are the project’s owner or a manager too. In a personal project all three are the project’s owner’s and managers’, as above. When you may, the line under the hint adds People you invite join Acme QA too., each row has its role list, and every row but yours a ✕:
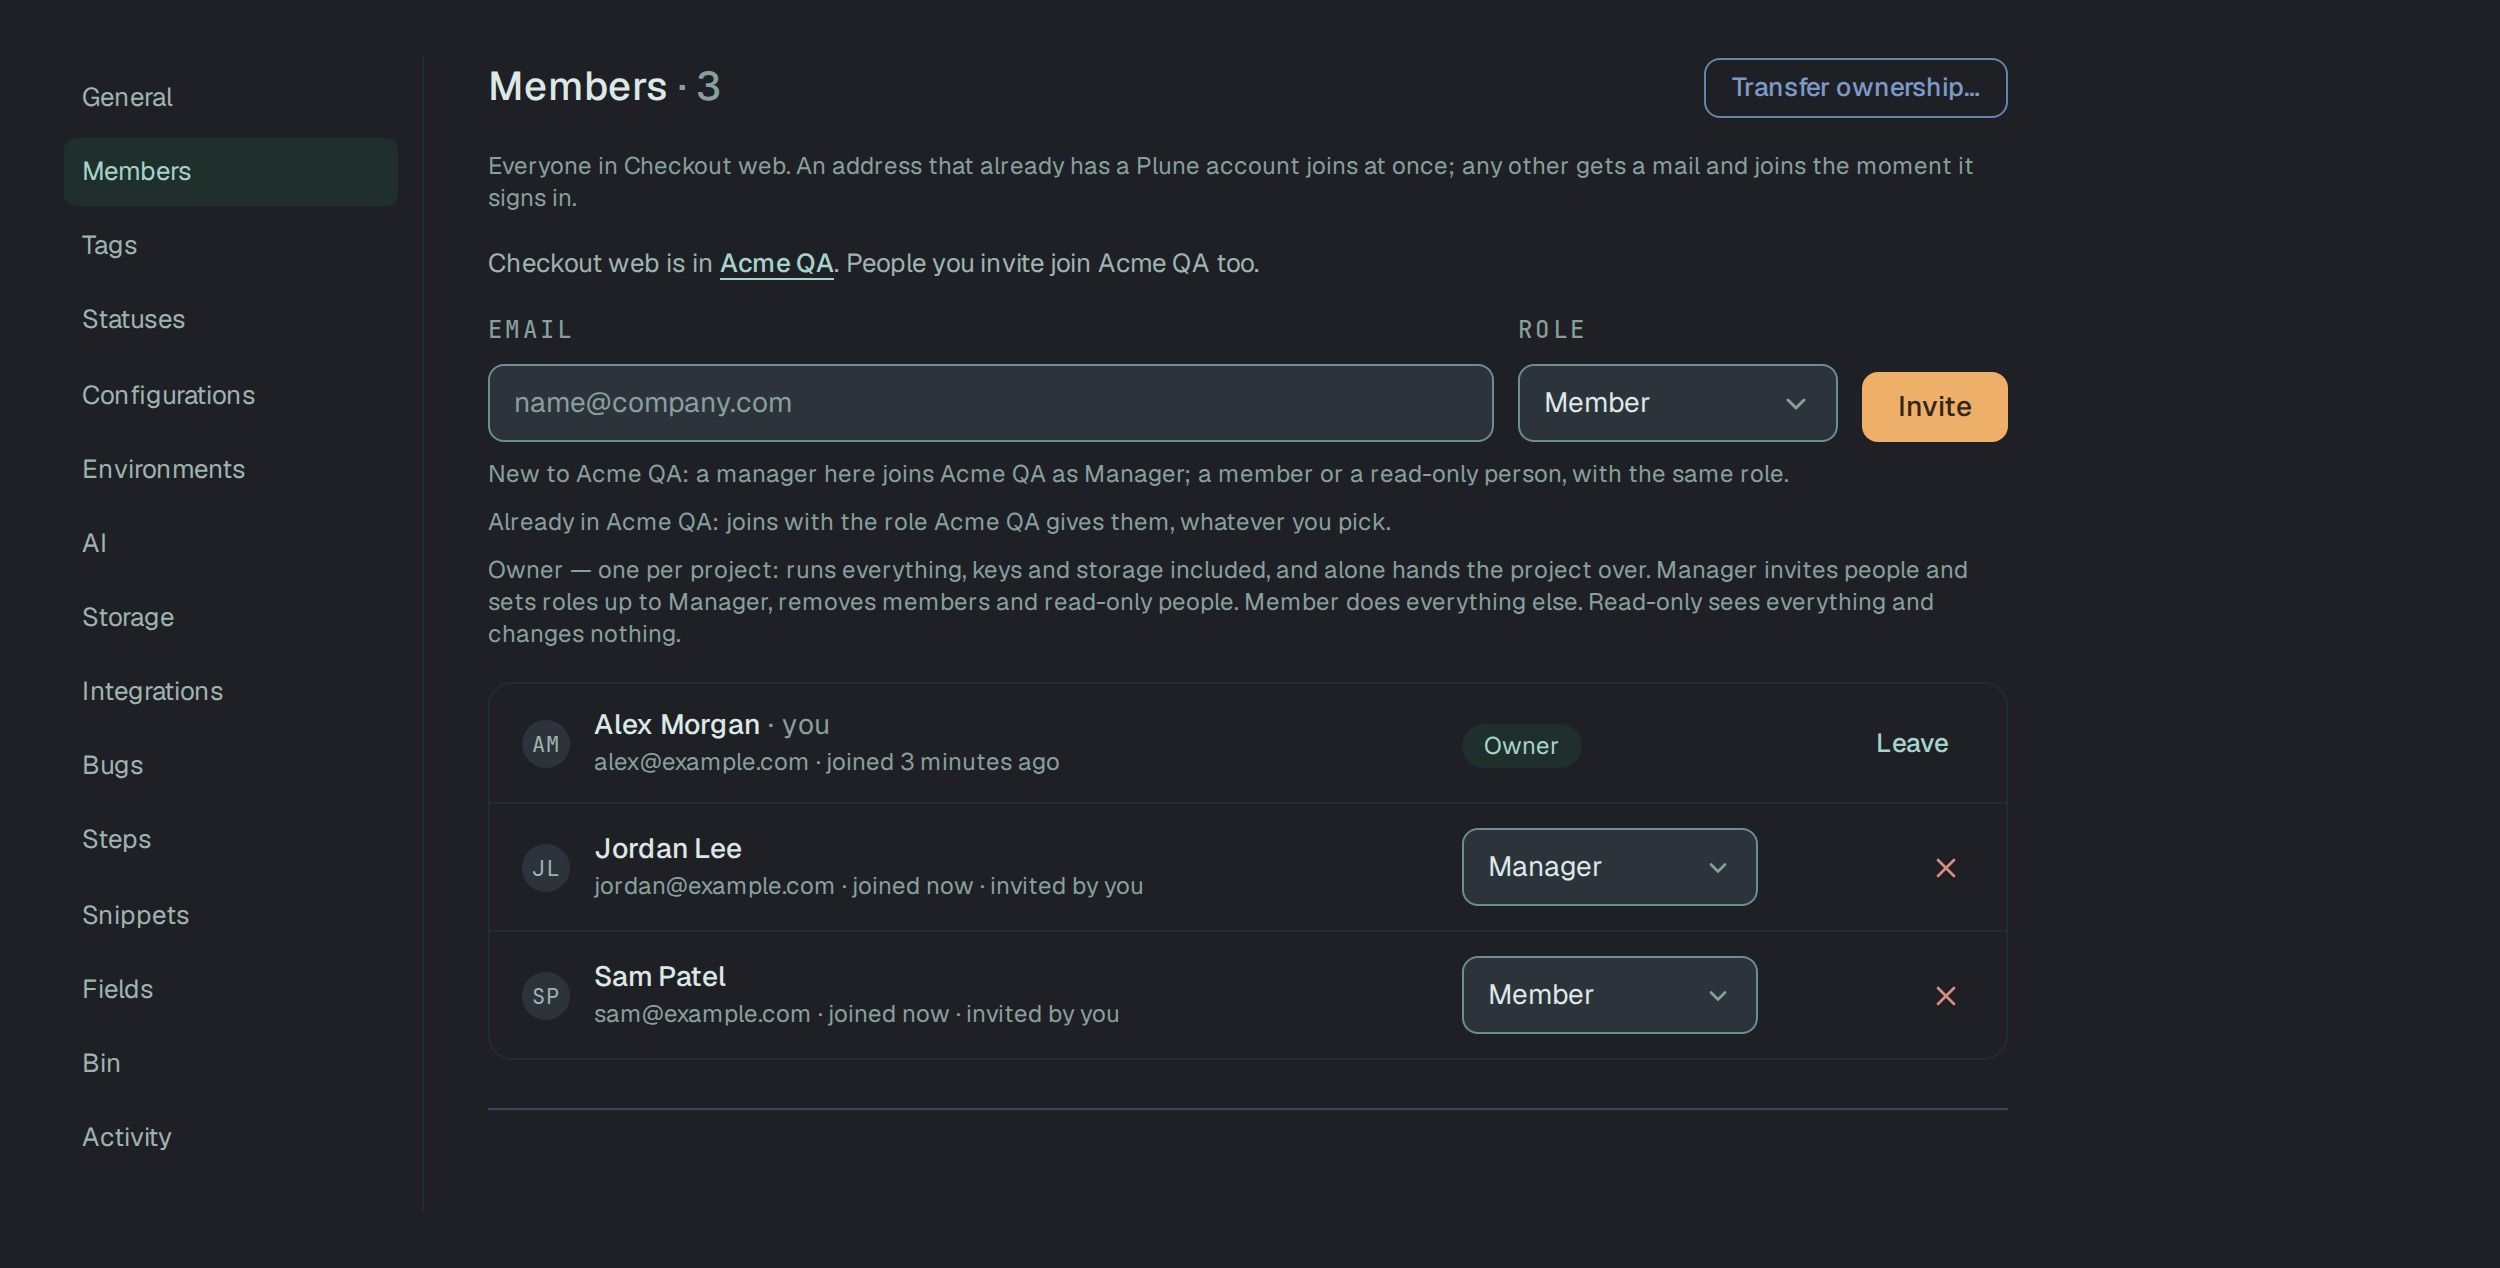
Who the invited person becomes. Somebody from outside the company is asked into the company as well, and two rules under the form tell how, both by the role you pick for them:
- New to Acme QA: a manager here joins Acme QA as Manager; a member or a read-only person, with the same role. — the company role follows the project role: Manager → Manager, Member → Member, Read-only → Read-only.
- Already in Acme QA: joins with the role Acme QA gives them, whatever you pick. — somebody already in the company joins the project with their company role’s project role and the pick is ignored.
Under the two rules stands the line the form has in every project: what each project role may do.
The answer is told apart exactly as in a personal project — ana@example.com joined Checkout web and Acme QA as Member. for an address that already had an account, Invitation sent — ana@example.com joins Checkout web and Acme QA at the first sign-in. for one that had not. An invitation this page sends is the company’s, so Revoke on its Pending row withdraws it through the company rather than through the project.
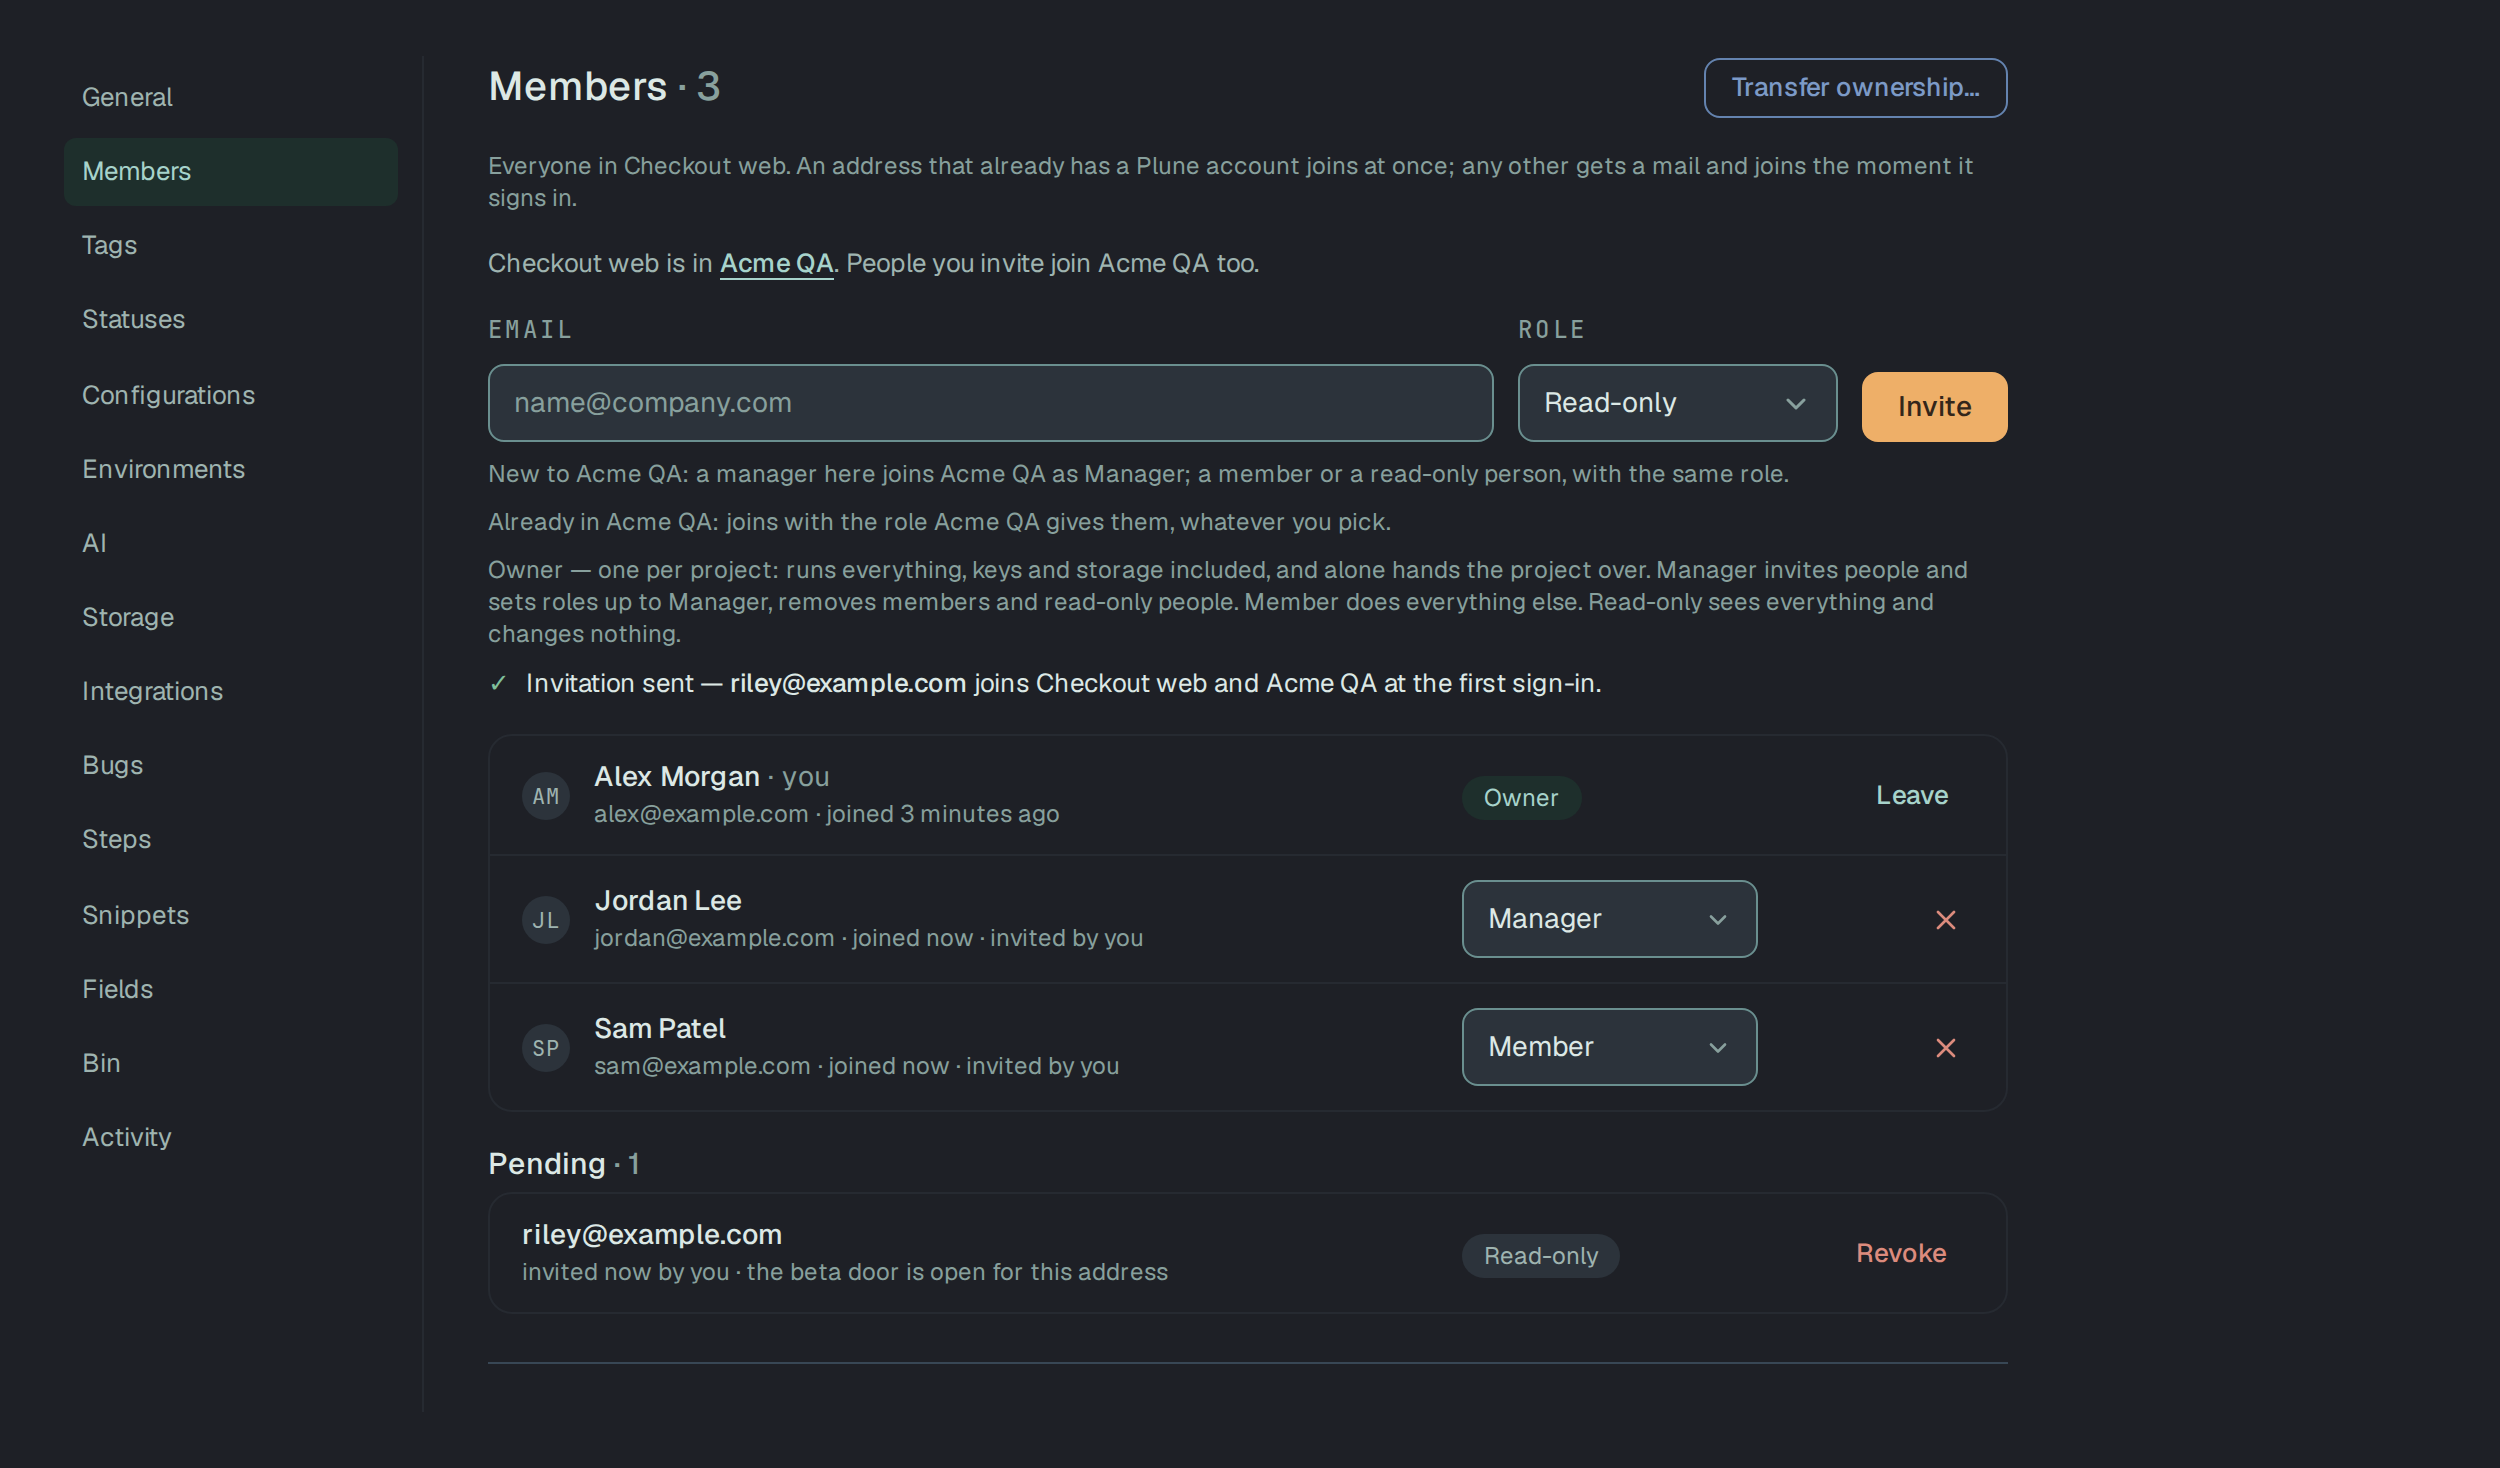
On a phone the form’s fields stand one under another, and each row puts its role list and ✕ under the name:
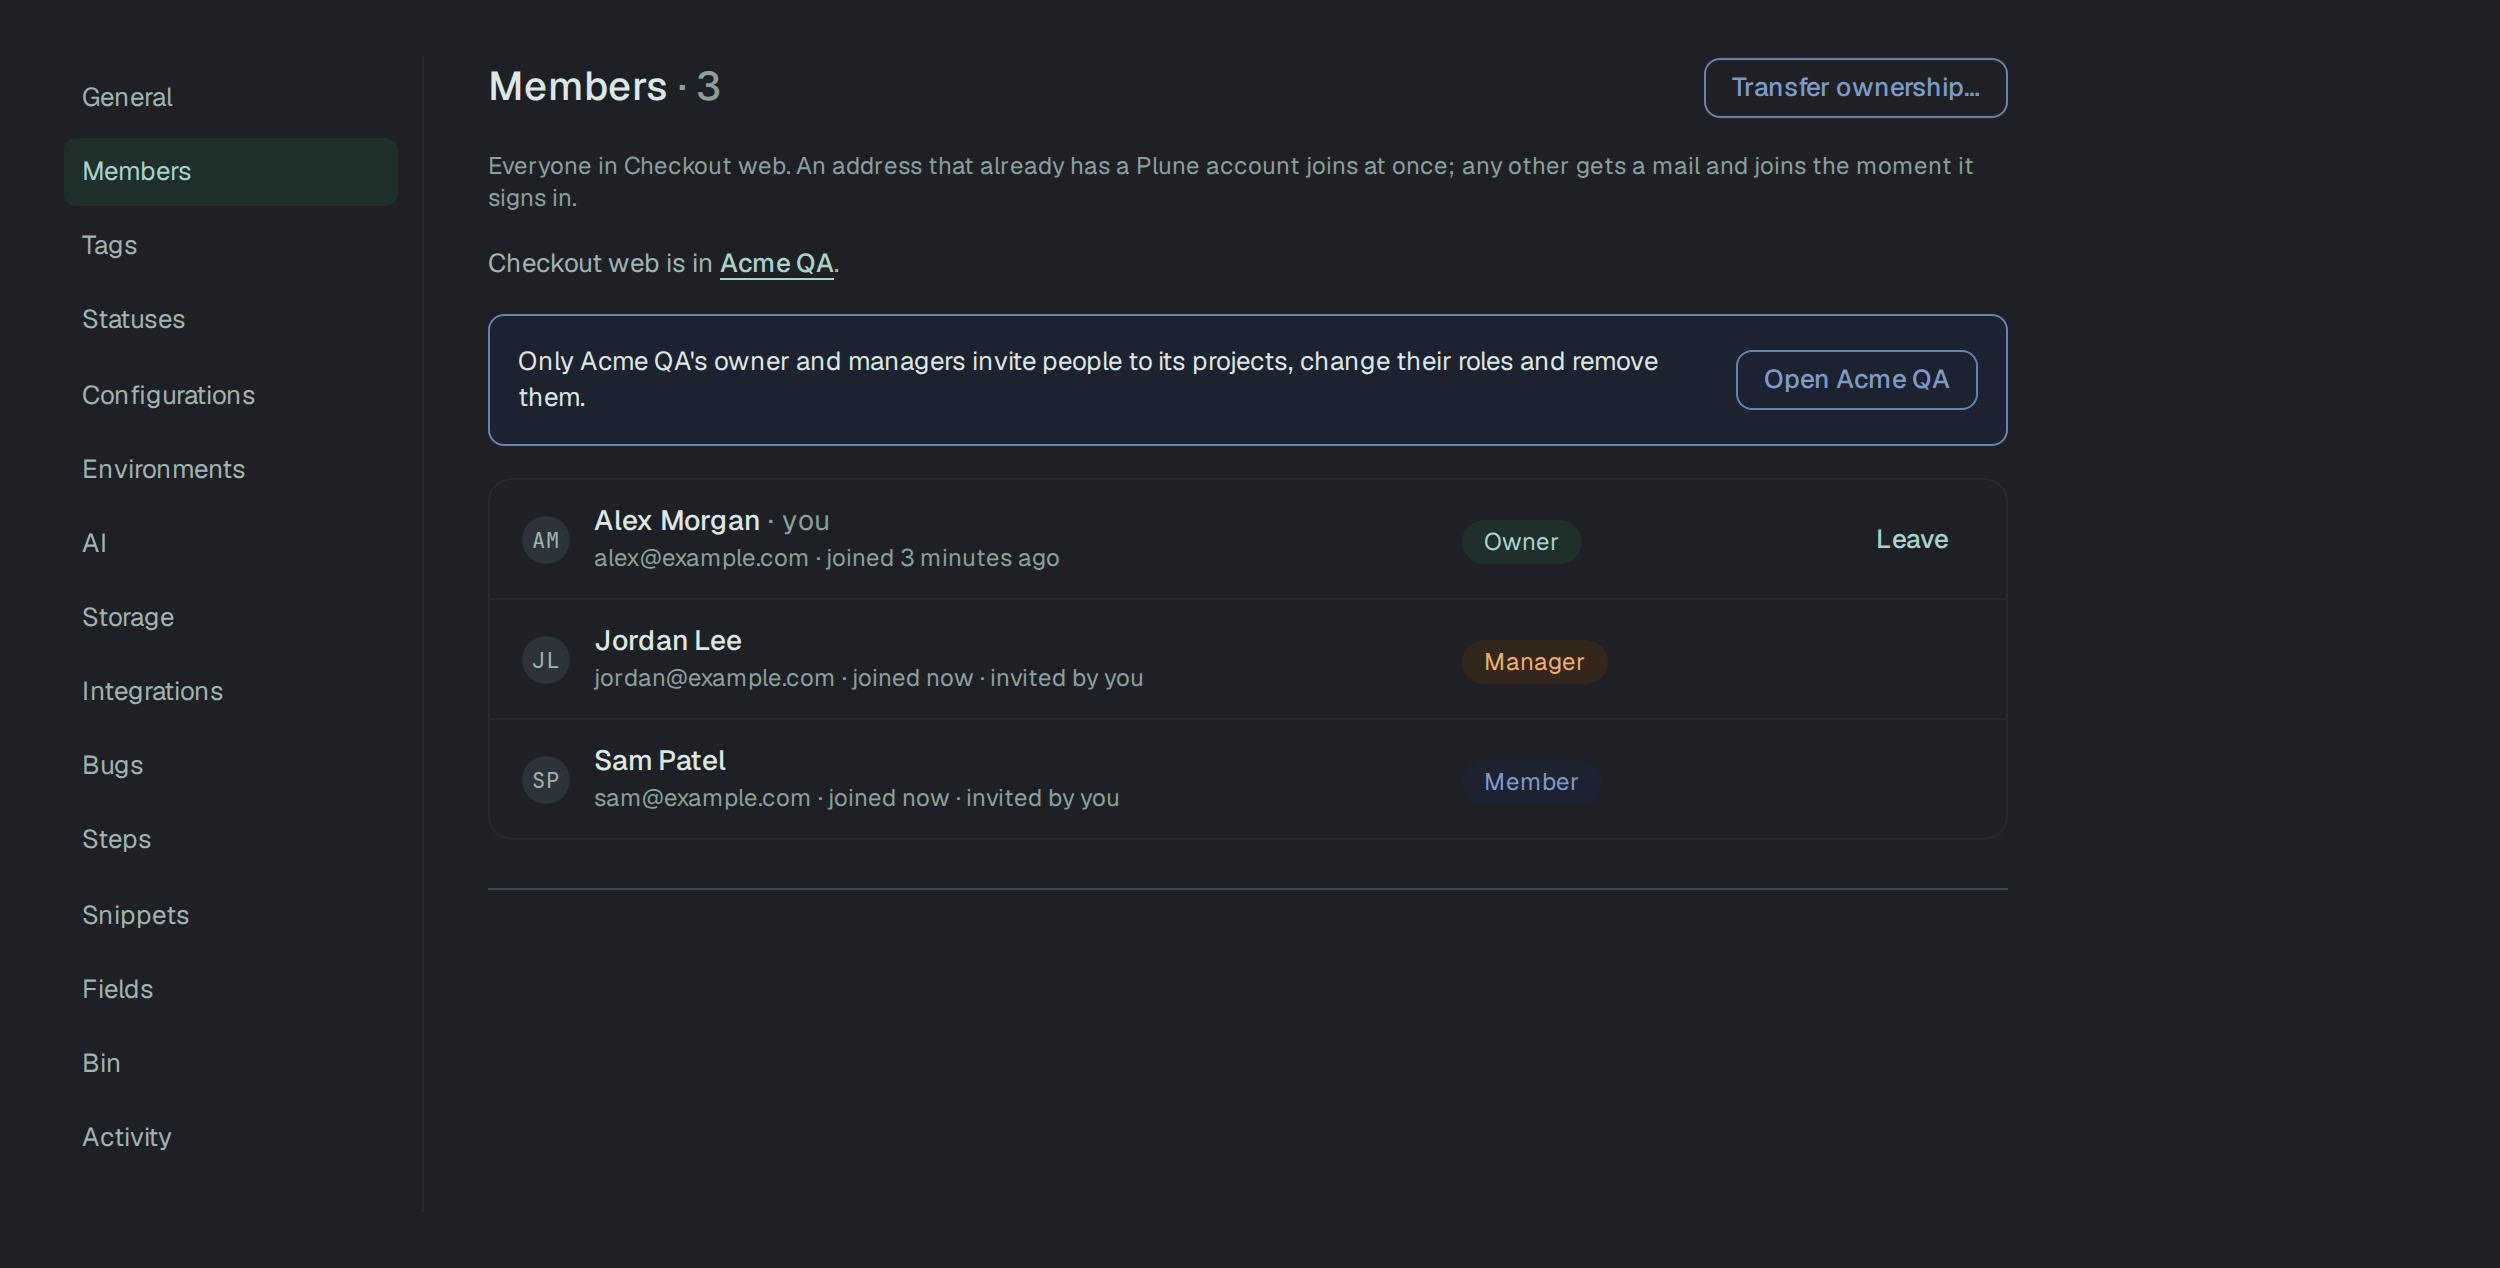
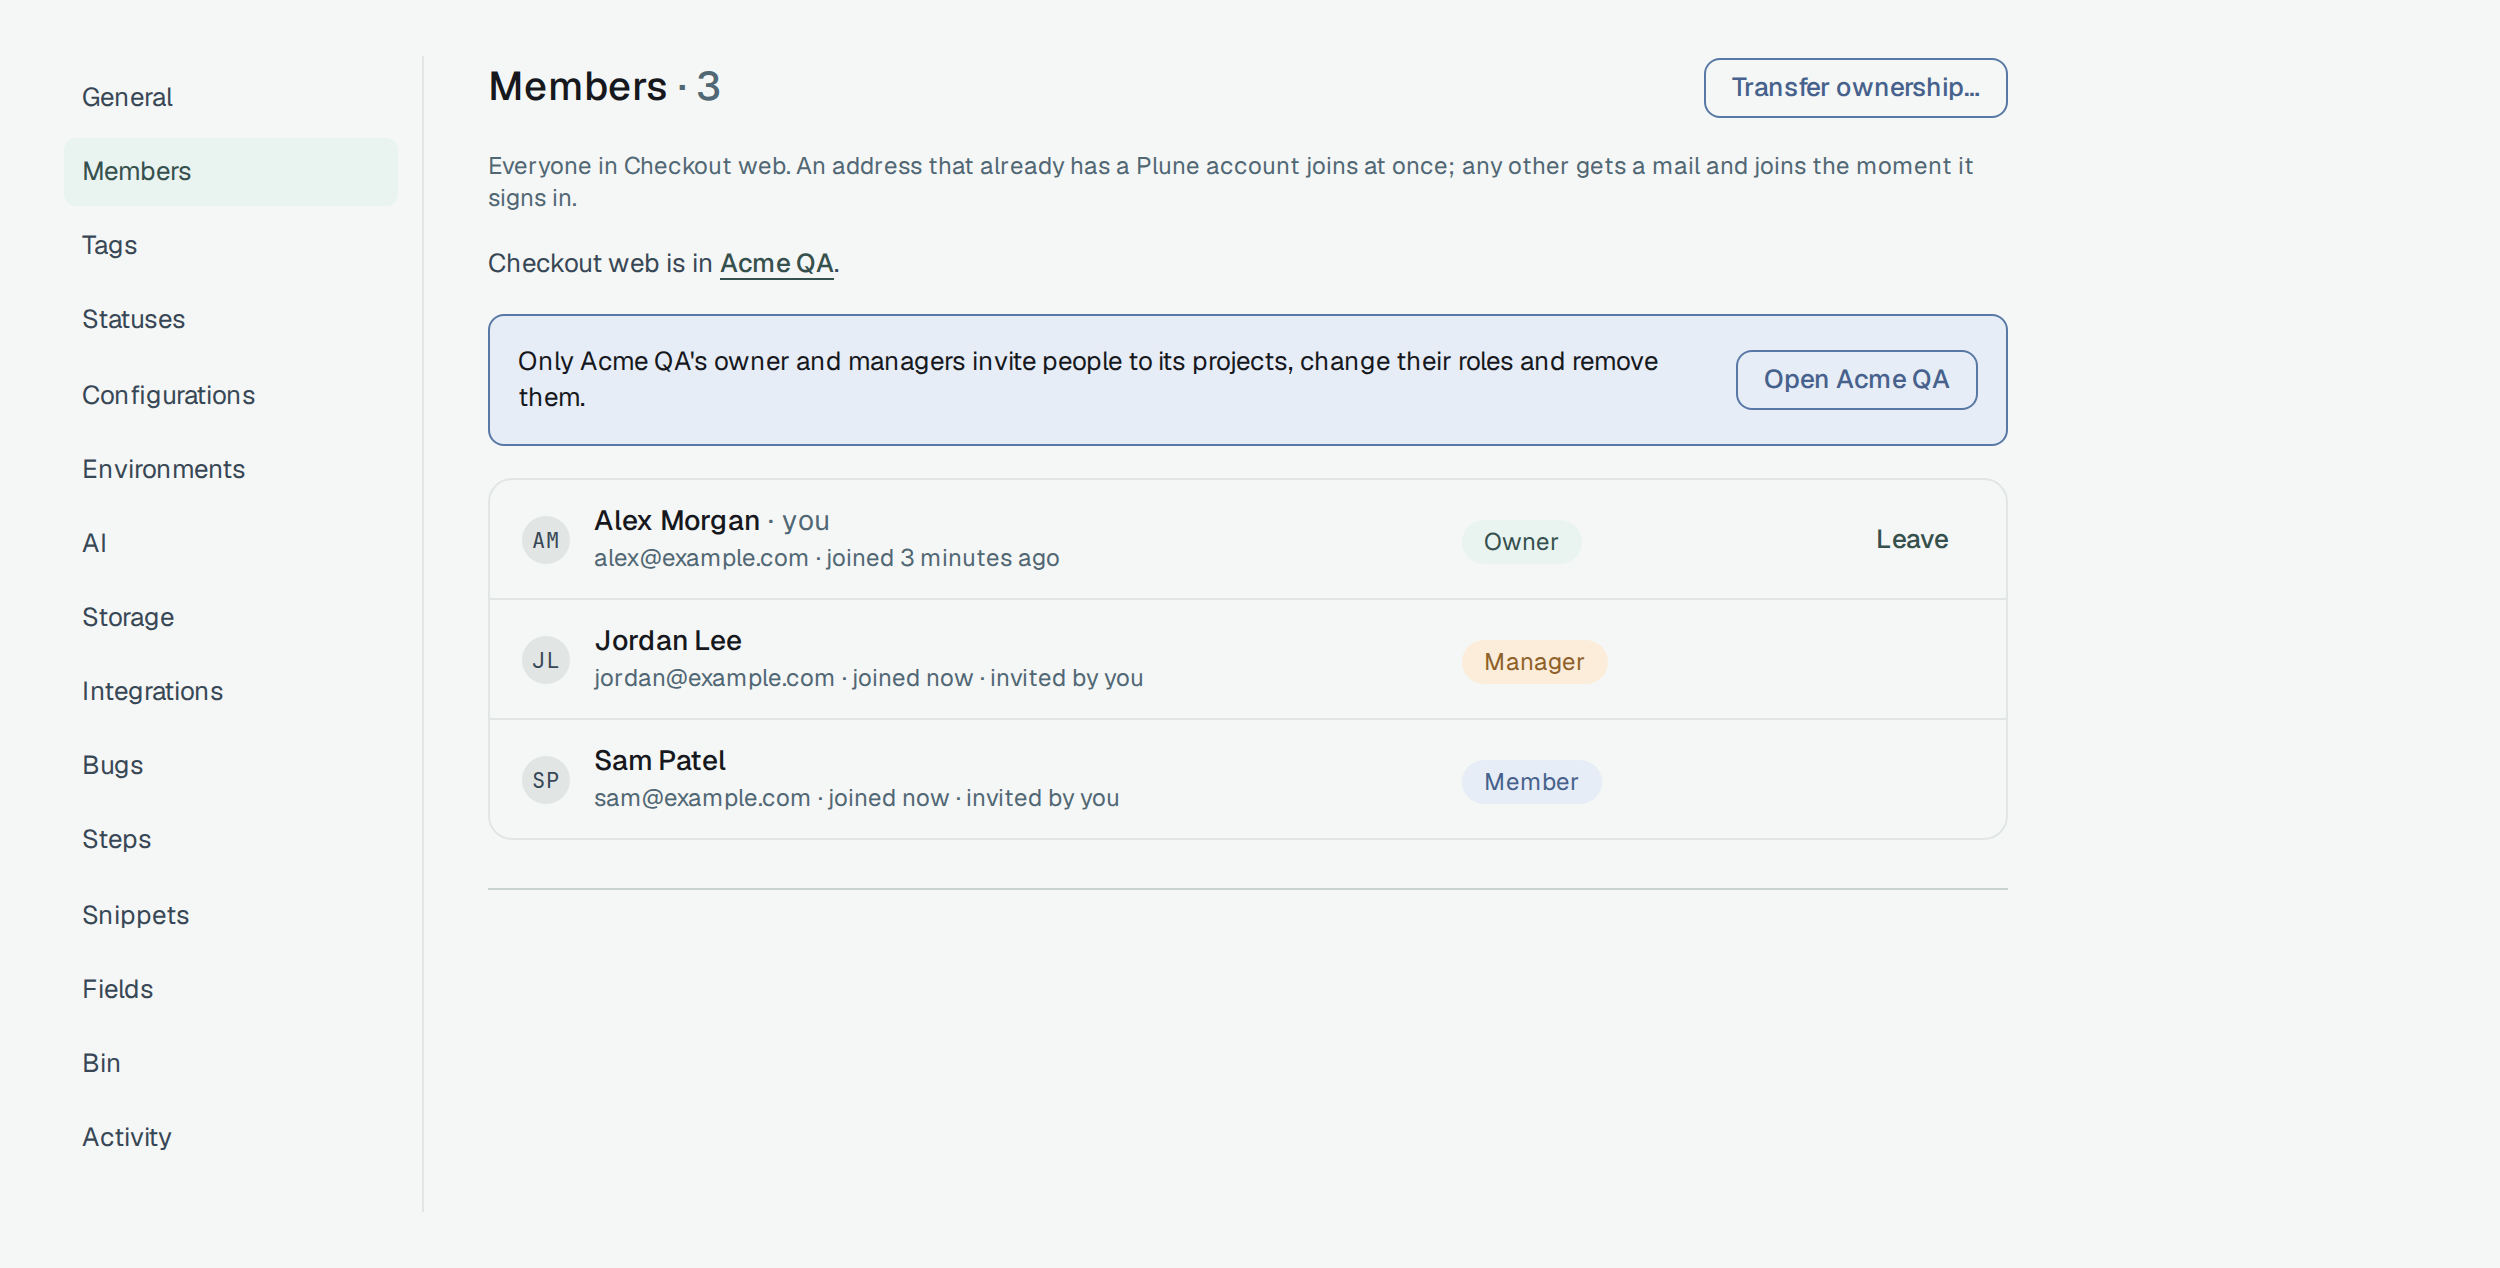
A project owner or manager with no company role. An owner or a manager of the project who is only a member or read-only in the company sees no form, no role list and no ✕: each role is a badge, and a notice names who may change them and opens the company — Only Acme QA’s owner and managers invite people to its projects, change their roles and remove them. with Open Acme QA. Leave stays on their own row, and so does Revoke on the Pending list. The same notice takes the controls’ place when a refusal arrives while the page is open, the company role having changed under it.
A member or a reader of the project sees neither form nor notice — they read the list, and their own row carries Leave.
Roles and removal
Section titled “Roles and removal”GET /v1/members → 200 { members: […], invitations: […] }PATCH /v1/members/{userId} { "role": "reader" } → 200 owner or managerDELETE /v1/members/{userId} → 204 owner or manager, or yourselfDELETE /v1/invitations/{id} → 204 owner or managerIn a company’s project the person must run the company too — above.
The rule is one for the whole project: give a role of your level and below; demote and remove only people strictly below you.
| Who acts | May give | May demote or remove |
|---|---|---|
| Owner | Manager, Member, Read-only | anybody but themself — a manager included |
| Manager | Manager, Member, Read-only | members and read-only people, not another manager and not the owner |
| Member, Read-only | nothing | nothing — only their own row, Leave |
A manager who reaches for another manager is answered 403 with the code
manager_cannot_touch_manager — a manager is demoted or removed by the owner only; anyone who
reaches for the owner, 409 owner_protected — the owner of the project is never demoted or removed.
A member asking to change somebody else’s role is answered 403 project owner or manager only; a
reader, 403 read-only member, at the boundary.
Any member may read the list — it is how a member finds out who to ask for a role. For the owner and managers each row has a role list and somebody else’s row a ✕, which asks once before it removes them; your own row carries Leave, which asks too. Everyone else sees each role as a badge. Somebody removed keeps nothing and loses nothing of the project’s: a case they wrote is the project’s, not theirs.
Transferring ownership
Section titled “Transferring ownership”The owner gives the project to somebody else with Transfer ownership…, on Settings → Members next to the list’s title.
- The owner asks. Pick New owner — anybody in the project (in a company’s project, somebody who is in the company too) — and click Send request. The dialog says what happens: the project stays where it is, only its owner changes; You become a manager: you keep managing people, and lose Storage, Integrations, AI keys, deleting from the Bin and handing over. The person asked gets a mail with a link to the request.
- Nothing changes until they accept. The request waits 7 days, one at a time per project. The owner can Cancel transfer; the person asked can Decline. A request nobody answers runs out and changes nothing.
- They accept. In one step the person asked becomes the owner and the old owner becomes a manager. Both are told by mail, and both changes are in the project’s audit feed. From then on only the new owner can hand the project over again — to anybody, including back to the previous one.
A request that no longer holds is cancelled rather than carried out. When the person asked is
demoted, leaves or is removed, it is cancelled at that moment, and accepting it then answers 404 —
handover ’…’ not found. When the owner changed since it was sent, or the project is gone, accepting
it cancels it and answers 409 — this handover no longer holds.
Only a person at the dashboard does this. The routes take the signed-in session, not an API token — a
CI’s token neither asks for, answers nor reads a handover (403):
POST /v1/projects/{id}/handover { "toUserId": "…" } → 202 { "handover": { … } } owner onlyDELETE /v1/projects/{id}/handover → 204 withdraw the open requestPOST /v1/handovers/{id}/accept → 200 the person askedPOST /v1/handovers/{id}/decline → 200 the person askedGET /v1/handovers/{id} → 200 the person asked, or the owner who askedA second request while one is waiting is 409 with the code handover_pending; a request while a
move to another company waits, 409 with the code
move_pending; asking yourself, 400;
somebody who is not a member of the project, 404. A company is handed over the same way — see
Companies → Transferring ownership.
Read-only
Section titled “Read-only”A reader reads every route a member reads and is answered 403 { "error": "read-only member" }
on every POST, PATCH and DELETE in the project, except three. The role is free, and
it reads, comments and proposes; approving needs a seat that writes. The third is the way out: a
reader may leave the project.
| A reader may | How |
|---|---|
| Comment on a case, a suite or a run | POST /v1/test-cases/{id}/comments, POST /v1/suites/{id}/comments, POST /v1/runs/{id}/comments — the comment is recorded with the reader as its author |
| Propose in the review queue | POST /v1/review-items — the item is created pending |
Everything else is 403 read-only member: approving or rejecting an item, editing, creating, muting
or deleting a case, creating a suite, starting a run, and taking a comment back (a reader cannot
Delete even its own). A reader of a project they are not in gets 404, as before.
On a case page the notice says so: You can view everything in Project, comment and send results to review. Changing and approving need write access — an owner can grant it on Settings → Members. Make member on the Members screen lifts the limit (Testomat’s «grant write access»).
A reader cannot mint a token either — minting is a write — so a read-only member reads reports in the dashboard, not through the CLI; see Projects.
What is recorded
Section titled “What is recorded”Every change of who is in the project lands in the project’s audit feed as an update of the
project entity, the address as the field: added tester@example.com as member, invited … as reader, olena@…: member → owner, removed …, … left, revoked the invitation of …. Who did it
and when are the feed’s own columns.
Names, and who did what
Section titled “Names, and who did what”A person is their address until they give themselves a name — on the Account page, «Your name» (the avatar at the top right → Profile):
PATCH /v1/me { "name": "Olena Kovalenko" } → 200 session only, like the tokensGET /v1/me → 200 { …, "name": "Olena Kovalenko" }One to 100 characters, trimmed; null clears it and the address stands in again. The name is what
every screen shows where a row names somebody — the Members list, the avatar’s initials in the top
bar, and the three records that now carry an actor:
| Record | Field | Set when |
|---|---|---|
| a case | createdBy | POST /v1/test-cases, and a duplicate — the caller, never the body |
| a run | createdBy | the first shard that created it — POST /v1/runs on either road, a plan’s launch, a Cairn ingest; a joining shard is not the creator |
| a result | executedBy | a source: manual result — whoever submitted it, then whoever last corrected it; a reporter’s result names nobody |
Each is a userId; the dashboard resolves them through GET /v1/members, which is why a reader
may read that list. The case page says created by Olena Kovalenko under the head, the run page
Launched by Olena Kovalenko in the run’s line, and a mark on the «To run» list reads by Olena
Kovalenko · 2 minutes ago. Somebody without a name shows as the local part of their address.
What else the team has
Section titled “What else the team has”Assigning a case to somebody: Cases → Assignee. Saying something about a case, a suite or a run, beside it: Cases → Comments. Notifications about either are not here yet.